DAIPAYAN
Available · Kolkata
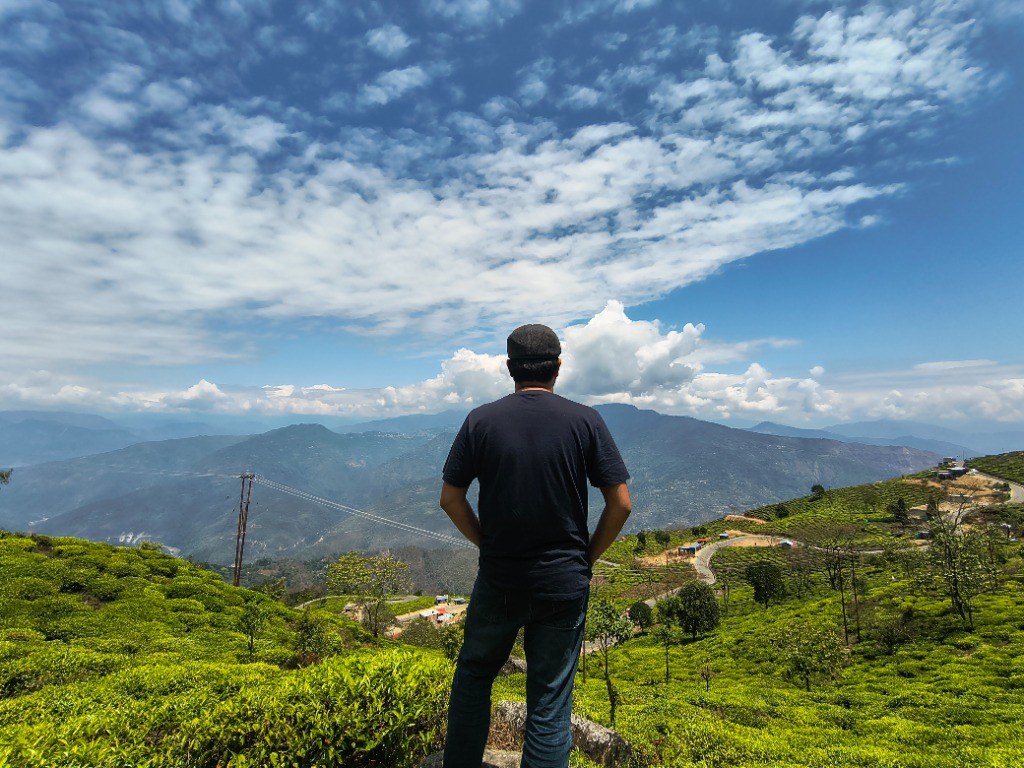
Mountain landscape overlooking tea hills and cloud cover
Open for Senior IAM · AppSec · AI Security
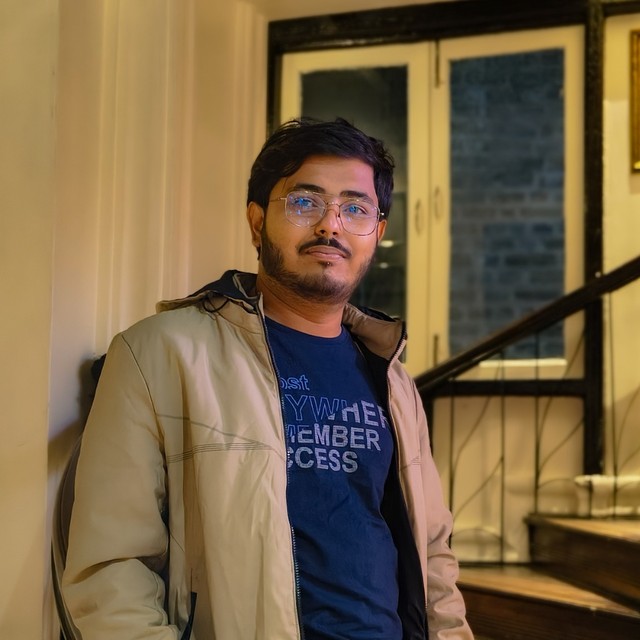
Portrait of Daipayan Ghosal
Kolkata, India · UTC+5:30

Daipayan Ghosal

Cybersecurity Analyst · IGA Architect & GenAI Builder

Wipro Limited Saviynt Certified (L200) 4 Springer Papers

Cybersecurity Analyst specializing in enterprise Identity & Access Governance (Saviynt IGA, Okta, Workday JML), Application Security (Checkmarx SAST, Secure SDLC), and AI Governance & Threat Defense (OWASP Top 10 for LLMs) alongside 4 peer-reviewed publications in neural computing.

01 · GITHUB & FEATURED BUILDS

Shipped Systems & Creative Labs

From evidence-grounded GenAI threat intelligence to dreamy narrative audio-story interfaces.

LIVE SECURITY APP

VulnInvestigator

Contextual vulnerability prioritization & threat investigation engine correlating NVD API v2, CISA KEV weaponization, and MITRE ATT&CK STIX 2.1 with grounded Ollama/Gemini RAG (<0.02% hallucination).

Python 3.12 Streamlit Ollama / Gemini RAG CISA KEV MITRE STIX 2.1
RISK WEIGHTING MODEL Kendall's τ & nDCG Verified
CVSS Severity Base35%
CISA KEV Weaponization30%
Asset Criticality20%
Network Exposure15%
LIVE AUDIO PLATFORM

Kahon Audio Sanctuary

Dreamy, Spotify-inspired web audio player facade built for audio storytelling channel @kahonstory — syncing 279+ stories, 39 playlists & 535+ hours with dynamic cover-art color-morphing ambience.

279+ Stories 39 Playlists 535+ Hrs Audio
TypeScript React / Vite Cover-Art Ambience @kahonstory Sync
VERCEL DEPLOYED

Creative Web Studio

Modern Next.js, TypeScript, and Tailwind CSS full-stack web studio crafted for fluid component interfaces and high-speed static/edge rendering.

Next.js TypeScript Tailwind CSS Firebase / Vercel
02 · ENTERPRISE ARCHITECTURE

Identity & Access Governance

End-to-end IGA workflows, automated JML lifecycles, and ITGC-aligned least privilege.

Lifecycle Automation (JML)

Engineered and managed automated Joiner-Mover-Leaver (JML) identity lifecycle workflows by integrating Workday HR platforms with Okta IAM environments.

Workday HR Okta IAM JML Automation

Identity Governance & RBAC

Overseeing end-to-end identity governance utilizing Saviynt IGA; designed role-based access control (RBAC) models and streamlined access certifications.

Saviynt IGA RBAC Models Access Certifications

Control Compliance & Least Privilege

Architected and maintained enterprise access control frameworks aligned with ITGC principles, embedding the principle of least privilege across business units.

ITGC Principles Least Privilege Risk Remediation

Workflow Integration & Audit Trails

Integrated ServiceNow workflows with identity solutions to create verifiable audit trails, structured provisioning paths, and enhanced corporate audit readiness.

ServiceNow Verifiable Audit Trails Audit Readiness
03 · APPLIED THREAT RESEARCH

AI Security & LLM Defense

Stress-testing prompt boundaries, mitigating algorithmic threat vectors, and securing agentic AI.

OWASP LLM Top 10 ↗

Local Red-Teaming (Ollama & R1)

Configured and deployed local AI models (Ollama, DeepSeek R1) via Google Colab in isolated environments to evaluate agentic AI vulnerabilities.

Prompt Injection Testing (LLM01)

Testing prompt structures and mapping findings to the OWASP Top 10 for LLMs to defend system prompts against adversarial manipulation.

AI Access Controls & DLP

Implementing Data Leakage Prevention (DLP) and role-governed access controls to protect sensitive training and inference data flows.

AI Risk Assessments & Governance

Conducting structured AI risk assessments and maintaining active awareness of regulatory frameworks such as the EU AI Act.

04 · CORE TOOLKIT

Skills & Technical Stack

Directly validated capability domains from verified enterprise security practice and research.

AI Security & Governance

LLM & RAG Security, Prompt Injection Testing, AI Risk Assessments, OWASP Top 10 for LLMs.

Identity & Access Governance

IAM, Saviynt IGA, Okta, JML Lifecycle, RBAC, AI Access Controls & Data Leakage Prevention (DLP).

Risk, Audit & Compliance

IT General Controls (ITGC), Control Evaluation, Audit Support, EU AI Act Awareness.

Application & Pipeline Security

Secure SDLC, DevSecOps, SAST (Checkmarx), Code Review, Python Scripting.

Vulnerability Management

Qualys VMDR, Penetration Testing, Incident Response, SLA Management.

Core Competencies

Process Optimization, Technical Reporting, Stakeholder Communication, Standard Operating Procedures (SOPs).

05 · CAREER JOURNEY

Professional Experience

Chronological enterprise experience across Identity Governance, AppSec, and applied research.

Oct 2025 – Present
Wipro Limited · Kolkata, IN

Cyber Security Analyst (IAM)

  • Identity Governance & RBAC: Oversee end-to-end identity governance utilizing Saviynt IGA; designed role-based access control (RBAC) models and streamlined access certifications to enforce strict compliance.
  • Control Compliance: Architected and maintained enterprise access control frameworks aligned with ITGC principles, embedding the principle of least privilege across business units.
  • Lifecycle Automation: Engineered and managed automated Joiner-Mover-Leaver (JML) identity lifecycle workflows by integrating Workday HR platforms with Okta IAM environments.
  • Risk Remediation: Proactively detected and mitigated critical access control gaps, significantly reducing risk exposure and enhancing corporate audit readiness.
  • Workflow Integration: Integrated ServiceNow workflows with identity solutions to create verifiable audit trails and structured access provisioning paths.
  • Stakeholder Alignment & Documentation: Partnered with HR, IT Operations, and Risk Governance teams to synchronize strategies; authored comprehensive documentation for system architectures and control procedures.
June 2022 – Oct 2025
Wipro Limited · Kolkata, IN

Cyber Security Analyst (AppSec & DevSecOps)

  • Risk Assessments & SDLC: Spearheaded application risk assessments during early-stage onboarding and secure SDLC integration to catch structural flaws before production.
  • CI/CD Pipeline Security: Evaluated and optimized security controls embedded within CI/CD pipelines, driving measurable maturity in automated pipeline defenses.
  • Vulnerability Management: Executed Static Application Security Testing (SAST) using Checkmarx; analyzed source code to discover vulnerabilities and partnered with engineers to guide remediation.
  • Audit & Liaison: Compiled detailed vulnerability findings, risk metrics, and mitigation actions to support corporate regulatory and compliance mandates; served as technical liaison between engineering and business stakeholders.
  • Process Optimization: Refined Standard Operating Procedures (SOPs) and governance documentation, accelerating process standardization across security practices.
2019 – 2023
Academic Research Track · India

Published AI Researcher (Neural Computing & Vision)

  • Peer-Reviewed Research: Co-authored 4 peer-reviewed Springer Nature & international conference publications in metaheuristic clustering, biomedical image segmentation, and computational intelligence.
  • Optimization & Modeling: Formulated chaotic fitness-dependent metaheuristic optimizers and rough-set clustering techniques in CIELab perceptual color space.
06 · PEER-REVIEWED PUBLICATIONS

Published Research

Springer Nature journals and international conference proceedings in computational intelligence.

Google Scholar ↗
2023 Springer · Neural Comput. Appl. 35 (21)

Chaotic fitness-dependent quasi-reflected Aquila optimizer for superpixel based white blood cell segmentation

Bio-medical segmentation combining chaos theory and fitness-dependent quasi-reflection with the Aquila Optimizer for white blood cell extraction.

DOI: 10.1007/s00521-023-08486-0 ↗
2022 Springer CCIS · Int. Symp. on AI

Concrete Crack Segmentation Using Histogram Based Fast Clustering and Morphological Operators

Unsupervised computer vision combining fast histogram clustering with morphological filtering to isolate concrete cracks at low computational cost.

DOI: 10.1007/978-3-031-22485-0 ↗
2022 Pleiades / Springer · Pattern Recognition 32

A comparative study among clustering techniques for leaf segmentation in rosette plants

Comparative evaluation of Rough K-Means against K-Means and Fuzzy C-Means in CIELab color space for plant phenotyping.

DOI: 10.1134/S1054661821040118 ↗
2021 Univ. of Maribor Press · 7th Student CS Conf.

Leaf Segmentation of Rosette Plants using Rough K-Means in CIELab Color Space

Early empirical formulation of rough-set clustering boundaries in CIELab perceptual color space for botanical image segmentation.

Google Scholar Index ↗
07 · VERIFIED CREDENTIALS

Certifications & Education

Industry security validations paired with computer applications foundations.

L200 ARCHITECT Saviynt · 2026

Saviynt IGA Level 200 Architect

Enterprise EIC Deployment, JML Lifecycle, Preventative SoD & Connectors

L100 ASSOCIATE Saviynt · 2026

Saviynt IGA Level 100

Identity Governance Architecture, Access Requests & Role Modeling

VMDR SPECIALIST Qualys · 2024

Qualys Certified Specialist — VMDR

Vulnerability Management, Asset Discovery & Prioritized Detection

C|EH v12 EC-Council · 2023

Certified Ethical Hacker (C|EH)

Penetration Testing, Threat Vector Assessment & Hardening

AZURE SC-200 Microsoft · In Progress

Security Operations Analyst (SC-200)

Microsoft Sentinel SIEM, Defender XDR & Incident Mitigation

BCA DEGREE 2019 – 2022 · 81.75%

Bachelor of Computer Applications

Midnapore College (Autonomous) · Vidyasagar University

08 · LET’S COLLABORATE

Connect with Daipayan

Open for Enterprise IAM / Saviynt Architect, AppSec & DevSecOps, and AI Threat Defense opportunities.